Observed EDRs
Last updated: November 26, 2025
Cork accelerates the warranty underwriting process by observing EDR agents installed on your clients' endpoints via your RMM connection. One your RMM is connected, Cork assesses the installed applications and you gain immediate insight into a key control coverage gap that is typically straightforward to resolve.
If Cork observes a valid EDR, that observation is represented by a blue checkmark. You can hover over the checkmark to expose the detected application:
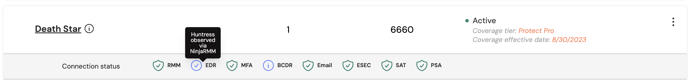
The list of EDRs Cork observes is below.
Software Name Contains | EDR Equivalent | Can Integrate? |
Webroot Secure Anywhere | Webroot | Yes |
SentinelOne | SentinelOne | Yes |
Cylance | Cylance | No |
Bitdefender | Bitdefender | Yes |
CrowdStrike * Sensor | CrowdStrike | No |
Check Point | Check Point Endpoint Security | No |
Huntress | Huntress | Yes |
Sophos (but not Sophos Connect) | Sophos | Yes |
Infocyte | Infocyte | Yes, Datto EDR |
ThorVigilance | Heimdal Security | No |
Malwarebytes Endpoint | Malwarebytes | No |
ESET Endpoint AntiVirus | ESET | Yes |
Vipre | Vipre | No |
Microsoft Defender for Endpoint | Microsoft Defender for Endpoint | Yes, through Microsoft Partner Center |
CynetEPS | Cynet | No |
Elastic Security | Todyl/Elastic | No |
WatchGuard Endpoint Agent, WatchGuard EDR Core | Watchguard | No |
SnapAgent | Blackpoint CyberSNAP | No |
TrendMicro Security | TrendMicro | No |
Cisco Secure Endpoint | Cisco Secure Endpoint (formerly AMP) | No |
Note: Cork still recommends connecting your EDR separately because it provides a distinct list of clients and endpoints to cross-correlate.
If your EDR is missing from this list, please reach out to us at support@corkinc.com. A member of our team will work with you to evaluate adding an observation and/or integration to meet your needs.